


Bring Your Own Device Policy: How to Secure Devices Within Microsoft 365


Every personal laptop and phone that reaches your corporate data is an endpoint you do not own and cannot fully account for. Bring-your-own device (BYOD) is now normal in large organizations, and it turns a simple executive question into a hard one: who can reach which data, from which device, and can you prove it?
With a Bring Your Own Device (BYOD) approach, employees can use their devices, such as laptops, smartphones, and tablets, for work. This strategy not only enhances productivity and employee satisfaction by enabling workers to use familiar devices, but it can also reduce costs for organizations by eliminating the need for company-issued hardware. Bring Your Own Device (BYOD) is a convenient option involving significant security risks. Personal devices tend to be less secure than those managed by an organization, making them more vulnerable to malware, data breaches, and unauthorized access. These risks become more pronounced when sensitive corporate information is accessed through unsecured networks or stored on personal devices without adequate security. Securing personal devices in an IT ecosystem like Microsoft 365 is crucial. Various tools such as Data Loss Prevention (DLP), Conditional Access, and Endpoint Management are essential in strengthening Bring Your Own Device (BYOD) security. DLP can prevent unintentional transfer of sensitive information outside the corporate network. At the same time, Conditional Access policies ensure that only the devices that meet the required security standards can access the network resources. Endpoint Management allows IT teams to enforce security policies remotely, manage device features, and secure data on personal devices. Together, these tools help safeguard the organization’s data and resources.
What is Bring Your Own Device (BYOD) (Bring-Your-Own-Device)?
Bring Your Own Device (BYOD) is a work policy that allows employees to use their devices, such as smartphones, tablets, and laptops, for work purposes. The policy has gained popularity in recent years due to its potential benefits. One of the most significant benefits of Bring Your Own Device (BYOD) is its increased productivity. Employees can use their devices to access work documents and information anytime and anywhere, making it easier to complete their tasks efficiently. In addition, Bring Your Own Device (BYOD) can also lead to higher employee satisfaction since it allows employees to use the device of their choice, which they may be more comfortable with and understand better.
However, Bring Your Own Device (BYOD) also comes with several challenges and security risks that organizations must consider. One of the most significant challenges is the need for device and data management. Since employees use their devices, organizations must ensure they have proper protocols to manage and secure the devices and data. It includes monitoring devices for malware, enforcing secure passwords, and encrypting data.
Bring Your Own Device (BYOD) can also lead to potential data breaches and loss, which can have severe consequences for organizations. For example, a lost or stolen device containing sensitive or confidential information could put the organization at risk of a data breach or compliance violation. Therefore, organizations must have clear policies and procedures to mitigate the risks associated with Bring Your Own Device (BYOD).
Understanding Bring Your Own Device (BYOD) Policies
The Bring Your Own Device (BYOD) policy allows employees to use their personal electronic devices for work-related tasks, offering flexibility and convenience that can increase productivity and satisfaction. However, when crafting Bring Your Own Device (BYOD) policies, it’s crucial to balance employee freedom with protecting sensitive corporate information. An effective Bring Your Own Device (BYOD) policy should specify which devices are allowed, define security protocols, and determine the boundaries between personal and professional data use.

Microsoft 365 provides robust security features that benefit organizations that implement Bring Your Own Device (BYOD) policies. These include advanced threat protection, data loss prevention, and identity and access management tools that integrate closely to protect corporate data and user privacy. Microsoft 365’s ability to manage and secure multiple devices and apps ensures that organizations can extend their security perimeter to include employee-owned devices without compromising the integrity of their IT infrastructure.
Data Loss Prevention (DLP) in Microsoft 365 is crucial for safeguarding sensitive information from being accidentally shared or maliciously exploited. DLP policies automatically detect and classify sensitive information across Microsoft 365 applications like Outlook, SharePoint, and Teams. When DLP rules are triggered, the system can take predefined actions, such as blocking data transmission or notifying administrators. It ensures that sensitive information such as social security numbers, credit card details, or confidential business data remains protected, even when accessed from personal devices.
Conditional Access is pivotal to Microsoft 365’s security framework, especially in a Bring Your Own Device (BYOD) context. This feature allows organizations to define and enforce policies that control access to corporate data and applications based on user, location, device state, and behavior. For instance, the organization might grant access only if the device complies with its security policies, such as having antivirus software installed and up to date. Conditional Access is critical for preventing unauthorized access and ensuring that only secure, compliant devices can connect to corporate resources. It allows businesses to embrace the flexibility of Bring Your Own Device (BYOD) while maintaining control over their data security, thus preventing potential breaches, and maintaining compliance with regulatory requirements.

Microsoft 365’s integrated tools and features enable organizations to implement Bring Your Own Device (BYOD) policies safely, protecting their resources and employees’ personal data from emerging threats.
Implementing Endpoint Management
Endpoint Management is a set of processes and technologies to secure and manage devices that access an organization’s network and data. These devices include laptops, tablets, smartphones, and other devices employees use in a Bring Your Own Device (BYOD) setting. Microsoft 365 offers endpoint management tools primarily managed through Microsoft Endpoint Manager, including Microsoft Intune and Configuration Manager. These tools enable IT administrators to ensure that the devices comply with corporate policies and security requirements.
Microsoft Endpoint Manager integrates directly with other Microsoft services, such as Entra ID and Microsoft Defender for Endpoint, to provide a unified and comprehensive security solution. This integration facilitates a range of security measures, including identity verification, access management, threat detection, and response actions. For example, Entra ID supports identity management and conditional access policies, while Microsoft Defender for Endpoint offers advanced threat detection, investigation, and response capabilities. This approach addresses all device and data security aspects across the Microsoft 365 environment.
Steps to Implement and Manage Endpoint Management
- Configure the Microsoft Endpoint Manager admin center to meet your organization’s requirements. Establish user groups and roles to manage permissions and access controls effectively.
- Establishing and enforcing compliance policies is essential to secure corporate resources and devices that can access them. These policies can include specific requirements such as password protection, encryption, and whether the device has been jailbroken or rooted. Furthermore, compliance policies help ensure that all devices are up to date with the latest security patches and operating system versions.
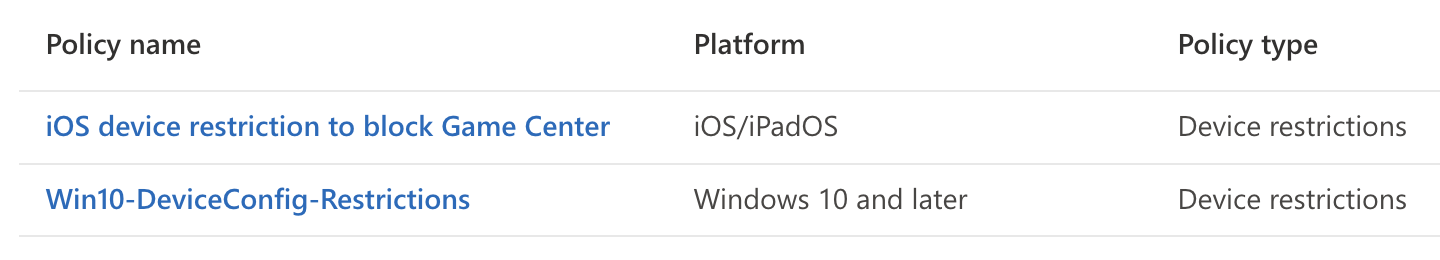
- You should implement a device enrollment program to enable employees to register their personal devices. This can be facilitated through a self-service portal, which will guide users through enrollment. To ensure that users can enroll their devices without compromising security, clear instructions and support should be provided.
- Configuring security settings is essential to ensure the security of your devices. It includes deploying firewalls, antivirus programs, and other threat protection services like Microsoft Defender for Endpoint. Additionally, you should configure data protection settings, such as DLP and app protection policies, to manage how data is accessed and shared on personal devices.
- It is essential to continuously monitor and manage all enrolled devices to ensure compliance with established policies. Microsoft Endpoint Manager offers analytics and reporting tools that you can use to track device status and compliance. Implementing automated alerts that notify administrators of non-compliance or security threats is recommended. It ensures prompt addressing of potential security issues.
- It is crucial to continuously update compliance policies and security configurations to keep up with new threats and evolving corporate standards. Additionally, users should receive ongoing training and support to help them maintain the security of their devices.

By following these steps, organizations can effectively implement and manage endpoint management within Microsoft 365, ensuring that personal devices used under Bring Your Own Device (BYOD) policies are secure, compliant, and optimally managed. This process protects corporate data and supports a flexible and productive work environment.
Example Bring Your Own Device (BYOD) Policies
To establish effective, Bring Your Own Device (BYOD) policies within Microsoft 365, it is crucial to create guidelines that balance security and usability. It is essential to focus on implementing policies within Microsoft 365 and planning and documenting the processes to support a secure and efficient Bring Your Own Device (BYOD) environment. These areas cover everything from security protocols to device management and will ensure a smooth and secure Bring Your Own Device (BYOD) experience for all employees.
Device Enrollment Policy:
Before accessing corporate resources, all personal devices used for work must be registered with the organization’s endpoint management system.
Authentication and Access Control Policy:
Multi-factor authentication (MFA) is required to access corporate data and applications from personal devices. Implement conditional access policies that evaluate the risk level based on the device’s compliance status, location, and user behavior.
Data Encryption Policy:
Encrypt all personal devices that store corporate data at rest, in use, and in transit to protect sensitive information from unauthorized access.
Device Compliance Policy:
Devices must meet specific security requirements to be compliant, such as installing antivirus software, enabling firewalls, and keeping operating systems up to date.
Application Management Policy:
Use Microsoft 365 application management tools to control personal device access to corporate apps and data.
Data Loss Prevention (DLP) Policy:
Implement policies to prevent unintentional data sharing outside the company. Monitor and control data movement across devices with DLP measures.
Incident Response Policy:
Outline the procedures to respond to a personal device security breach. Include the steps for remote data wiping if the device is lost or stolen.
Privacy Policy:
It is essential to communicate how the organization will access, monitor, and manage personal devices used for work while respecting employee privacy rights.
Software Update Policy:
All personal devices used to access corporate data must run the latest approved versions of operating systems and software to ensure protection against vulnerabilities.
Exit Strategy Policy:
Establish a protocol for securely wiping corporate data from personal devices when an employee leaves the company or is no longer part of the Bring Your Own Device (BYOD) program.
When clearly defined and effectively implemented, these policies help ensure that Bring Your Own Device (BYOD) practices within Microsoft 365 enhance productivity without compromising security.
Conclusion
Supporting Bring Your Own Devices (BYOD) requires policies such as Data Loss Prevention (DLP), Conditional Access, and Endpoint Management to build a robust security framework. Implementing comprehensive governance for Bring Your Own Device (BYOD) is crucial because it ensures that all security measures are consistently applied and adapted to the evolving threats and changes in the work environment. Organizations should adopt these practices to enhance their security posture and foster a culture of security awareness and compliance.
Organizations can leverage the benefits of the Bring Your Own Device (BYOD) trend while ensuring their security needs are met by integrating strong security practices with a robust governance model. This dual approach will help establish a secure, flexible, and resilient digital workplace where productivity and protection are equally important.
A note from Rencore
Examples of sensitive information that can be controlled from leaking outside your organization include financial data or personally identifiable information (PII), such as credit card numbers, social security numbers, or health records. With measures such as setting up Data Loss Prevention (DLP) policies and a robust overall Microsoft 365 governance strategy, you can safeguard your organization from these security risks.
BYOD is a risk question before it is a device question, and risk is the pillar it ladders to. Rencore’s Digital Workplace module complements and extends the controls you already run in Microsoft Intune, Entra, and Purview: it inventories the workspaces, sites, and files a personal device can actually reach, ranks risky sign-ins and external sharing by exposure, and turns that into an action your IT team can take rather than another dashboard to read. If you want to go further on the security posture of your Microsoft 365 estate, download our free whitepaper titled ‘ Understanding Microsoft Cloud Services and Security.’
Last updated 11 June 2024


